
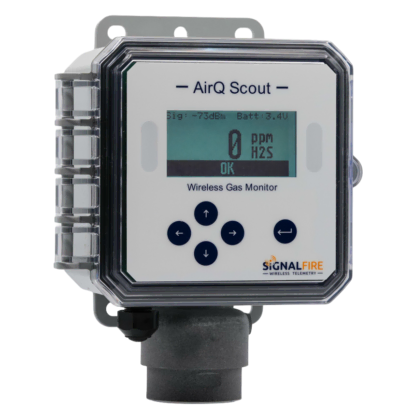
AirQ Scout-LCD AirQ Scout-LCD
Explore its connectivity and integration capabilities or request a quote today.
Oil & Gas
SignalFire Telemetry products connect you with crucial product and hardware data at any of your oil and gas operation sites—whether it’s a pump, pipeline, or storage tank.
Water & Wastewater
SignalFire Telemetry devices install anywhere water asset monitoring is needed, whether it’s for collection purposes, treatment, or delivery.
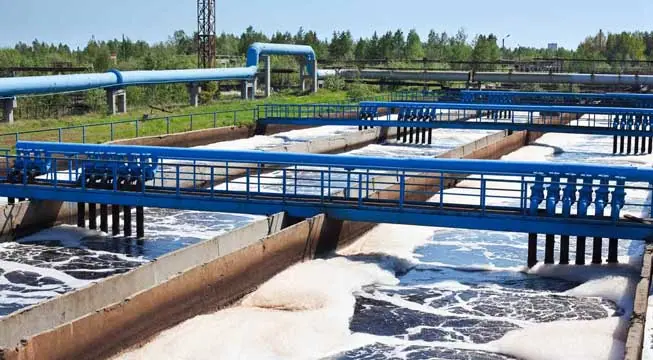
General Industrial
SignalFire Telemetry devices can monitor key assets and can do it affordably, without any renovation or high-priced engineering costs. They install easily with no required cable or additional power. The data is available on your phone or computer and the cloud service can even output to your corporate system to integrate with the rest of your data and keep your operation running.
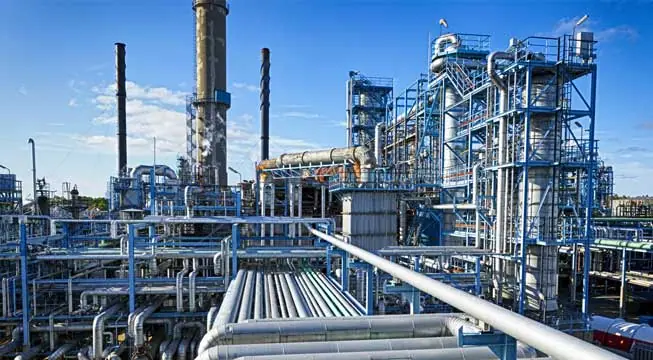
Agriculture
SignalFire Telemetry devices can monitor and manage water supplies and additives throughout the property, helping you avoid catastrophic shortages and keep your irrigation plan on track.
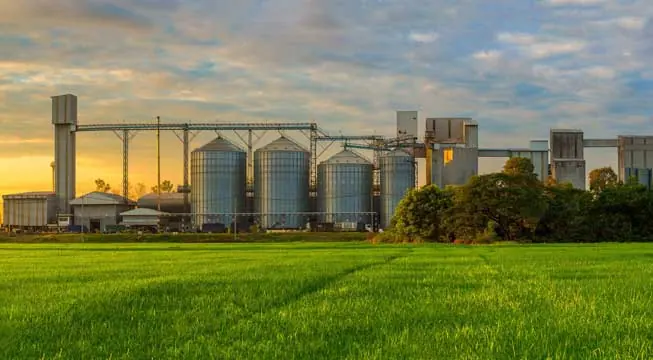
Tanks & Terminals
Avoid costly product loss in bulk storage tanks, terminals, and transportation movements. Whether calling for tank levels, gauge pressure, or even movement pumps or pipelines, SignalFire products can fill any monitoring gap throughout a facility.
Environmental
Environmental fines for businesses are frustrating and can bring business to a standstill until they’re worked out. No business wants to hurt the environment, and in competitive markets stopping production affects the bottom line and staff. But there are effective and affordable solutions with SignalFire Telemetry devices.
Refining & Petrochemical
Expand visibility and control of your refinery or petrochemical processing facility without expensive renovations or redesigns. And do it with your current gauges and hardware. SignalFire telemetry devices are designed to work in harsh chemical environments and meet the strictest safety and security standards
Utilities
No matter the size of your service map, monitoring remote assets ensures efficiency and keeps your operation in compliance. That’s how SignalFire devices can really help, offering the most affordable and effective monitoring solution that will monitor liquid, gas, electricity, and other assets.
Document Center
Browse all documentation pertaining to SignalFire products.
Cloud Setup
Have a RANGER? Set up your Cloud account here.
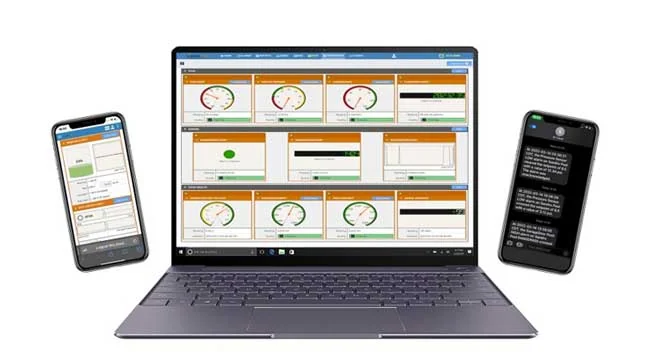
Case Studies
Explore the diverse applications of SignalFire Wireless Telemetry Systems across different industries.
Brochures
Access our latest brochures to explore comprehensive information about our products and services.
Commonly Supported Sensors
Easily find the sensors that are compatible with our systems on this dedicated page.
Photos
Explore a comprehensive collection of images showcasing our products, installations, and real-world applications.
News & Articles
Stay up to date with the latest content from SignalFire.
Videos
Explore our video library.
Software Downloads
Get access to the RANGER and SignalFire Toolkit Software.
Contact Tech Support

Recent cyber incidents have targeted water and wastewater utilities across at least seven states, disrupting operations by changing PLC passwords, modifying network settings, and locking operators out of internet-connected equipment. In response, federal agencies are urging utilities to disconnect vulnerable PLCs from the public internet and strengthen protections around operational technology.
These incidents reinforce an important message for every industrial organization: Any internet-facing device can become a potential entry point when ports are exposed, default credentials remain in place, or access is not properly controlled.
Remote monitoring can provide significant operational benefits, but convenience should never come at the expense of protection. Organizations must understand how their equipment communicates, where potential vulnerabilities exist, and what safeguards are being used throughout the system.
A network port is a communication point that allows data to travel to or from an internet-connected device.
Think of a PLC as a bus carrying process data. The ports are like windows that allow information to move in and out. When those windows are properly secured, the system can communicate as intended. When a port is unnecessarily exposed to the public internet, however, an attacker may have an opportunity to access the device.
This is particularly concerning in industrial environments because exposed ports may provide a path to PLCs, controllers, sensors, network equipment, or other operational assets.
Two ports commonly associated with industrial networks include:
When industrial communication ports are publicly exposed or incorrectly configured, unauthorized users may be able to monitor network activity, intercept traffic, or send malicious commands to connected equipment. SignalFire recommends working with both OT and IT teams to ensure internet-facing ports are closed, protected by appropriate firewall rules, and accessible only by trusted systems.
Open ports are only one part of the risk. Weak, reused, or default credentials can also leave industrial systems vulnerable.
Many PLCs and industrial devices are initially configured with credentials that are published in product manuals or readily available online. When those credentials are never changed, an attacker may not need sophisticated tools to gain access.
Organizations should establish password policies that include:
Cybersecurity is most effective when technology, access policies, and employee practices work together.
SignalFire’s RANGER family of cellular IIoT transmitters connects field data from supported sensors and instrumentation to SignalFire Cloud or a compatible private MQTT platform. RANGER devices communicate over LTE-M or NB-IoT cellular networks.
Unlike an industrial device that accepts unsolicited connections through a publicly exposed port, the RANGER initiates its own outbound connection to a configured MQTT broker. It does not accept direct inbound connections from the public internet.
The process works as follows:
As a result, SignalFire Cloud communicates with the RANGER through the established MQTT broker connection rather than through a direct public connection to the device.
Cellular networks use standard encryption to protect communications between a device and the cellular network. However, cellular encryption alone does not automatically provide end-to-end protection from the field device to the final data destination.
That is why SignalFire uses TLS 1.2 to encrypt communications between the IIoT device and the MQTT broker. This additional encryption helps protect data as it travels through the communication path rather than relying solely on the cellular connection.
This layered approach helps provide:
SignalFire Cloud uses Amazon Web Services infrastructure rather than locally hosted SignalFire servers.
According to SignalFire’s IIoT cybersecurity architecture, stored data is protected using AES-256 encryption with encryption-key management, while transmitted data is protected using TLS encryption. This adds another layer of security after data reaches the cloud environment.
The complete communication path includes protections at multiple stages:
RANGER IIoT device → encrypted cellular communication → MQTT broker hosted through AWS infrastructure → SignalFire Cloud
No single security measure should be expected to protect an entire industrial system. Layered security helps reduce risk by protecting the device, the communication channel, the cloud infrastructure, and user access.
Protecting information in transit is only part of the cybersecurity equation. Organizations must also control who can view, manage, and modify their operational data.
SignalFire Cloud allows organizations to create individual user profiles and grant specific permissions based on each person’s responsibilities. Rather than providing every employee with the same level of access, administrators can limit users to the functions needed to perform their jobs.
SignalFire Cloud also supports two-factor or multi-factor authentication. Administrators can require it for all users, selected users, every login, or after a defined period of inactivity. Because the feature requires user configuration, SignalFire strongly encourages organizations to enable and enforce it for all applicable accounts.
Even when a password is compromised, two-factor authentication can provide an additional barrier by requiring a second form of verification.
Technology can provide important safeguards, but cybersecurity must remain a shared responsibility across operations, engineering, IT, management, and equipment providers.
Organizations should regularly review:
Understanding the complete communication path, from the field device to the cloud, is an essential first step toward reducing risk.
Remote visibility does not have to require exposing industrial equipment directly to the public internet.
SignalFire’s RANGER IIoT architecture combines encrypted cellular communication, outbound MQTT publishing, TLS encryption, cloud-based data protection, user permissions, and optional two-factor authentication to help organizations securely monitor critical process information.
Is your IIoT infrastructure protected?
Contact SignalFire to discuss secure wireless sensing, monitoring, and telemetry solutions for your operation.
Explore its connectivity and integration capabilities or request a quote today.


